OKX battles multimillion-dollar thefts after SIM-swap attacks

OKX battles multimillion-dollar thefts after SIM-swap attacks

user avatar

by Eve Adams

2 years ago


The cryptocurrency exchange OKX and its security partner SlowMist are investigating a major exploit that resulted in the theft of assets from two users.

The investigation pertains to the theft of two accounts on the OKX exchange, which occurred on June 9 through a SIM-swap attack. This information was reported by Yu Jian, founder of SlowMist, in a post on X.

The risk notification via SMS came from Hong Kong, and a new API key was created (with permissions for withdrawals and trading, so we initially suspected cross-trading intentions, but now that seems unlikely).

Although the exact amount of stolen funds is unknown, Jian noted that “assets worth millions of dollars were stolen.”

SlowMist: 2FA is Not the Main Issue in the Attack

The security firm SlowMist continues to investigate the incident, and the exchange’s two-factor authentication (2FA) mechanisms may not be the primary vulnerability.

In a post on X dated June 9, Yu Jian wrote:

“I did not enable a 2FA authenticator such as Google Authenticator, but I am not sure if this is the key point.”

According to the analysis by the Web3 security group Dilation Effect, OKX’s 2FA mechanism allowed the attackers to switch to a less secure verification method, enabling them to whitelist withdrawal addresses through SMS verification.

However, more experienced hackers have begun to bypass 2FA methods. In early June, a Chinese trader lost $1 million due to fraud involving a Google Chrome ad plugin called Aggr. This plugin steals users' cookies, which are then used by hackers to bypass passwords and 2FA.

Increase in Phishing Attacks

In June, the number of phishing attacks increased after CoinGecko confirmed a data breach on its third-party email management platform GetResponse. As a result of the breach, the attacker sent 23,723 phishing emails.

Phishing attacks aim to steal sensitive information such as private keys of cryptocurrency wallets. Some attacks, known as address poisoning scams, trick investors into voluntarily sending funds to fraudulent addresses similar to those they have previously interacted with.

Leaks of private keys and personal data have become the main cause of cryptocurrency-related breaches, as attackers target the easiest victims.
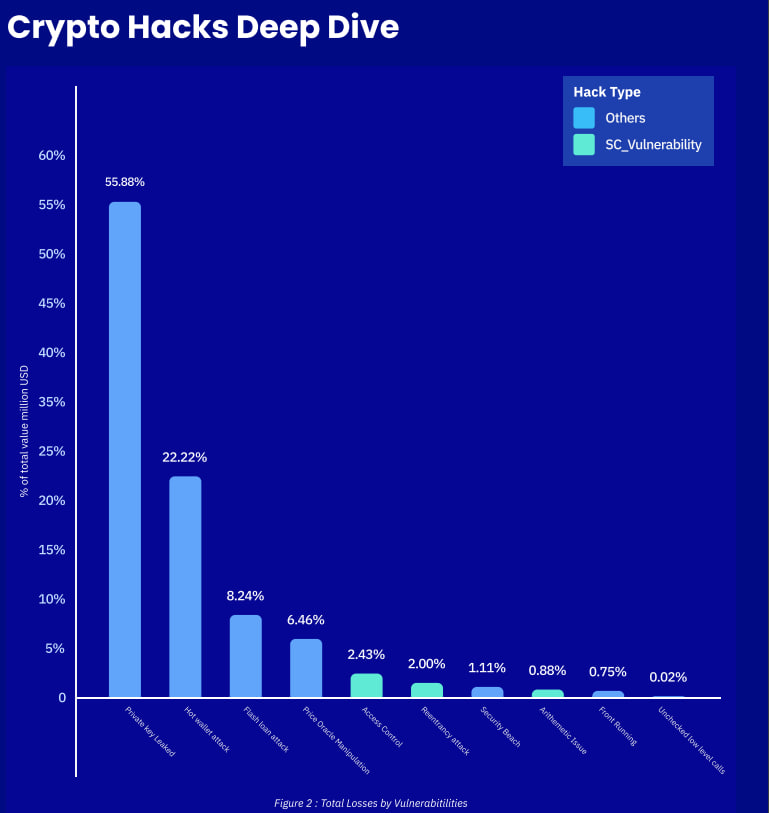
Overall cryptocurrency losses due to vulnerabilities

According to the HackHub report by Merkle Science for 2024, over 55% of hacked digital assets were lost due to private key leaks in 2023.
Tier I

Sector: #18291

Sealed Hiding Place Room

Resource Cache

Resource Cache

Tier I

Requires 25% Tier Progress to Claim
Meme Cache

Meme Cache

Tier I

Requires 50% Tier Progress to Claim
Equipment Cache

Equipment Cache

Tier I

Requires 75% Tier Progress to Claim

After collecting, hiding places will be stored in your inventory and can be opened with Keys.

Other news

CF Benchmarks Introduces CFB Oracle to Enhance On-Chain Price Integrity

CF Benchmarks has launched CFB Oracle, a service providing cryptographically signed index information for applications on Ethereum mainnet, HyperEVM, and Robinhood Chain.

user avatarLuis Flores

SEC Proposes New Custody Framework for Crypto Assets

The SEC has proposed a new custody framework for investment advisers and registered funds dealing with crypto assets, allowing for potential self-custody and the use of state trust companies as custodians.

user avatarArif Mukhtar

FINMA Approves First Swiss Retail Bitcoin ETF

Switzerland's financial regulator, FINMA, has approved its first retail ETF that invests directly in Bitcoin, allowing retail investors to gain regulated exposure to Bitcoin.

user avatarMaria Gutierrez

EIP7906 Proposal Considered for Enhancing Ethereum Transaction Safety

The Ethereum Foundation is considering EIP7906, which proposes a readonly post-transaction frame to evaluate changes and events before accepting transaction outcomes.

user avatarDavid Robinson

Ethereum Foundation Investigates Enhancements to Transaction Safety

Researchers at the Ethereum Foundation are examining native transaction assertions to enhance transaction safety and reliability in digital asset markets.

user avatarAndrew Smith

Ethereum Developers Delay Glamsterdam Upgrade on Hoodi Testnet

Ethereum developers have postponed the Glamsterdam upgrade initially scheduled for the Hoodi testnet on October 26, with no new activation date provided.

user avatarJacob Williams

Important disclaimer: The information presented on the Dapp.Expert portal is intended solely for informational purposes and does not constitute an investment recommendation or a guide to action in the field of cryptocurrencies. The Dapp.Expert team is not responsible for any potential losses or missed profits associated with the use of materials published on the site. Before making investment decisions in cryptocurrencies, we recommend consulting a qualified financial advisor.