
According to a report published on July 10 by Spreek, an on-chain investigator and Twitter user, an individual is utilizing the Multichain Executor to deplete tokens linked to the AnySwap bridging protocol. This recent report comes after the Multichain team flagged "abnormal" outflows exceeding $100 million from Multichain bridges on July 7.
Based on the July 10 report from Spreek, there has been a recent incident involving the Multichain Executor address. The report states that the address has been draining various anyToken addresses across multiple blockchain networks and transferring them to a new externally owned account (EOA).
The report includes an image that displays an Ethereum transaction with the hash 0x53ede4462d90978b992b0a88727de19afe4e96f0374aa1a221b8ff65fda5a6fe. By analyzing the blockchain data, it was discovered that this transaction invoked the "anySwapFeeTo" function on the Multichain Router: V4 contract. As a result, around $15,275.90 worth of anyDAI, which is a derivative version of the Dai stablecoin, was created on the Ethereum network and subsequently sent to the Multichain Executor. The Multichain Executor then burned the received anyDAI tokens and exchanged them for the underlying DAI tokens that back the anyDAI asset.
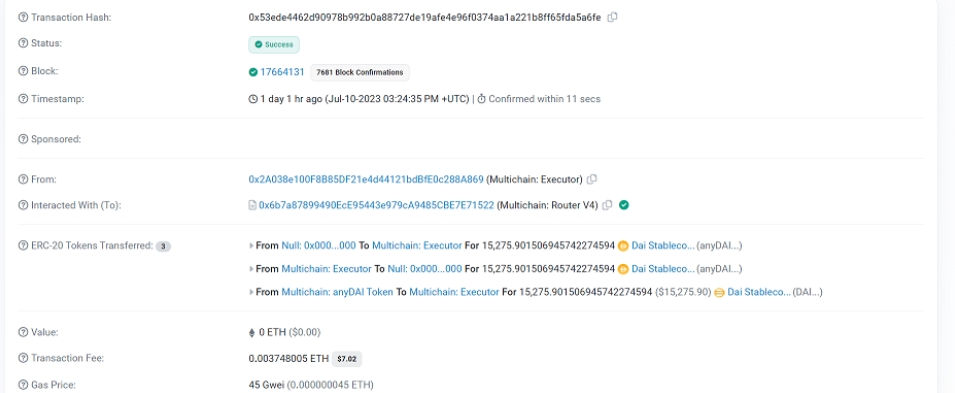
DAI conversion by the Multichain Executor.
In a separate comment, Spreek mentioned that the funds are being transferred to the following address: 0x1eed63efba5f81d95bfe37d82c8e736b974f477b. According to Ethereum blockchain data, this address received the redeemed DAI from the Multichain Executor on July 10, approximately five minutes after the previous transaction.
According to data from the BNB Smart Chain (BSC), the Multichain Executor executed the anySwapFeeTo function on its network, converting approximately $208,997 worth of anyUSDC tokens. The resulting tokens were then exchanged for Binance-Pegged USDC and sent to the same address. Additionally, in other BSC transactions, the contract utilized the same process to convert 50.80 anyBTC, valued at $39,251.43 at the time, into Binance-Pegged Bitcoin and sent it to the aforementioned address.
In total, these transactions amount to approximately $263,524.33 worth of tokens transferred to the specified address using the anySwapFeeTo method.
Spreek mentioned that this conduct could be a regular aspect of the protocol's operation. However, a separate account had exhibited comparable behavior the previous day, according to Spreek's statement. Eventually, that account sold the depleted tokens, thereby presenting proof of its malicious intent:
The on-chain investigator known as the "sleuth" has put forward a theory suggesting that the attacker behind the Multichain incident might be exploiting the anySwapFeeTo function. This function allegedly allows the setting of fees to an exceedingly high amount, enabling the attacker to drain users' funds. According to Spreek, the function permits the choice of the total value of the token held in that particular anyToken, as it seemingly accepts any value.
Blockchain analysts have been puzzled by the Multichain incident, as there is no conclusive evidence to determine whether it resulted from an exploit or if it was simply a case of large tokenholders transferring their funds across networks. The mystery unfolded on July 7 when more than $100 million worth of tokens were withdrawn from the Ethereum side of Multichain's bridges—specifically those connected to Fantom, Moonriver, and Dogechain—and sent to wallet addresses with no transaction history. These withdrawals accounted for the majority of funds held on each bridge.
The Multichain team acknowledged the withdrawals as "abnormal" and advised users to refrain from using the protocol. However, they did not disclose the exact cause or potential sources of this anomaly.
On July 8, Circle and Tether, two issuers of stablecoins, froze certain addresses that had received funds linked to the peculiar transactions. On July 11, blockchain analytics firm Chainanalysis stated that the incident appeared to be more consistent with a hack or rug pull rather than a straightforward migration.
Furthermore, the Multichain team has reported that their CEO is missing, and they have also shut down some bridges due to the unavailability of certain servers within the network's multi-party computation setup.